
Security, Hardened Guardrails & HMAC Signatures
Security, Hardened Guardrails & HMAC Signatures
Security is the #1 priority when allowing external AI models to interact with a self-hosted WordPress website. Insecure implementations that execute raw shell commands or transmit plaintext administrative credentials leave servers vulnerable to devastating breaches.
Digent Smart AI is architected around an uncompromising Bank-Grade Encrypted Security Model with zero stored passwords, anti-replay cryptographic signatures, and granular permission enforcement.
[!IMPORTANT] Enterprise Banking-Grade Cryptography:
Every request between your AI client and WordPress is authenticated using SHA-256 HMAC cryptographic signatures and verified within a strict ±300-second timestamp drift tolerance window.
Enterprise Cryptographic Handshake Protocol
The diagram below details the cryptographic verification and security layers executed on every single tool call:
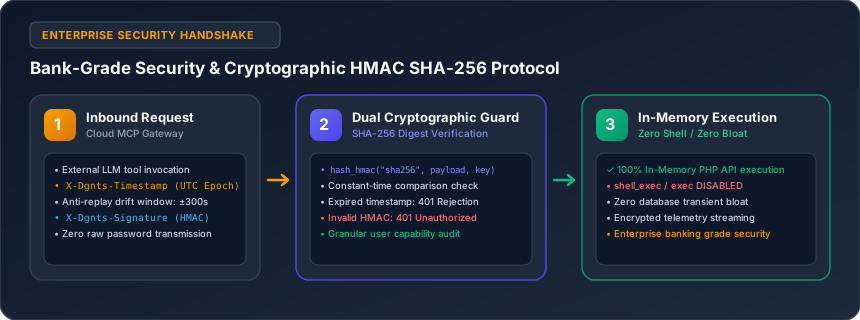
The 4 Security Pillars of Digent Smart AI
1. Granular WordPress Capability Enforcement
Every single tool invocation verifies the authenticated user's native WordPress capabilities before executing:
edit_posts/publish_posts: Required for creating, updating, or drafting content.edit_theme_options: Required for injecting CSS or modifying theme files.manage_options: Required for administrative configurations and database cleanups.moderate_comments: Required for comment approvals and spam trashing.
An AI client cannot perform any action that the authenticated user does not have permission to execute manually.
2. Cryptographic HMAC SHA-256 Signatures
When paired with the Digent Smart AI Cloud Gateway, every HTTP request contains two mandatory cryptographic security headers:
X-Dgnts-Timestamp: Unix epoch timestamp in UTC seconds (enforces a strict ±300-second anti-replay window).X-Dgnts-Signature: Cryptographic HMAC SHA-256 digest calculated across the HTTP method, request URI, timestamp, and payload body using your site's shared secret.
Requests with expired timestamps or invalid signatures are rejected instantly with HTTP 401 Unauthorized before any WordPress code runs.
3. Zero Shell Execution (shell_exec Disabled)
Unlike insecure developer plugins that run raw bash commands on your operating system, Digent Smart AI's administrative bridge operates 100% in-memory using WordPress internal PHP APIs (WP_Plugin_Dependencies, get_plugins(), wp_delete_post()).
Dangerous PHP execution functions like shell_exec(), exec(), system(), and passthru() are strictly forbidden and never used. This makes Digent Smart AI 100% compatible with shared hosting, managed WordPress hosts (WP Engine, Kinsta), and locked-down container environments.
4. Zero Database Bloat Architecture
Traditional audit plugins write millions of log entries directly into your wp_options or wp_posts tables, causing database bloat and slow backups.
Digent Smart AI streams execution latency metrics, tool call logs, and telemetry directly to your Cloud Gateway dashboard without writing transient logging rows to your local MySQL database.
Security Audit Checklist
| Security Feature | Standard Dev Plugins | Digent Smart AI |
|---|---|---|
| Authentication | Stored plaintext passwords | Cryptographic HMAC SHA-256 |
| Shell Access | Raw shell_exec() / bash |
100% In-Memory PHP APIs |
| Error Containment | Fatal WSOD on syntax error | Isolated try/catch mu-plugins |
| Backup Protection | Manual manual backups | Automatic timestamped theme snapshots |
| Permission Model | Full root / admin bypass | Granular WordPress capability checks |
| Anti-Replay Window | None (Vulnerable to replay) | Strict ±300s timestamp tolerance |
Related Guides in Maintenance, Security & Developer Engines
Have questions or need technical support?
Our engineering team is ready to help you connect your AI agents.